
Loading story…
A new MacSync malware-as-a-service campaign targets macOS cryptocurrency users and developers with trojanized DMG applications, binary loaders, and droppers. Originally advertised as Mac.c in 2025, the stealer has progressed from AppleScript payloads to Swift and Objective-C binaries and now uses Apple iCloud Calendar and file-hosting infrastructure to retrieve subsequent payloads.
MacSync collects browser and cryptocurrency-wallet data, credentials, Keychain-related material, Telegram data, cloud and developer configuration files, system details, and shell histories. It persists through LaunchAgents, modified ZSH settings, global Git hooks, Login Items, and restoration scripts while suppressing user notifications; its backdoor can receive C2 tasks to install browser extensions, replace Ledger wallet software, repeat collection, and potentially intercept browser traffic.
Pull IOCs and campaign context straight into your stack.
4 events from the most recent confirmed update back to the earliest known activity.
Researchers first observed an updated MacSync campaign using malicious DMG application bundles, binary loaders and droppers, and iCloud Calendar and file-hosting infrastructure to deliver later-stage payloads. The campaign included Toria cryptocurrency-wallet impersonation and deployed an infostealer and Objective-C backdoor with extensive persistence and data-theft capabilities.
The macOS information and cryptocurrency stealer was advertised under the name Mac.c on dark-web forums before its developers renamed it MacSync.
A Gurucul threat-research report documented MacSync persistence through LaunchAgents and Git hooks in addition to ZSHRC modification, along with AES/ECDH Curve25519 use, anti-debugging, and in-memory execution. The report published 21 MD5 hashes and malicious URL indicators tied to MacSync infrastructure and payload delivery.
A Huntress-documented MacSync Stealer/RAT intrusion temporarily modified the victim's ~/.zshrc so that a Base64-wrapped curl | zsh command would run when the victim next opened an interactive zsh Terminal session. The exact command was not published.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 56 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
11 references tracked. Mallory keeps watching after this page renders.
xakep.ru
Open sourcecommunity.gurucul.com
Open sourcehelpnetsecurity.com
Open sourcecybersecuritynews.com
Open sourcesecurelist.ru
Open sourcesecurelist.com
Open sourcedfir.ch
Open sourcetheevilbit.github.io
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
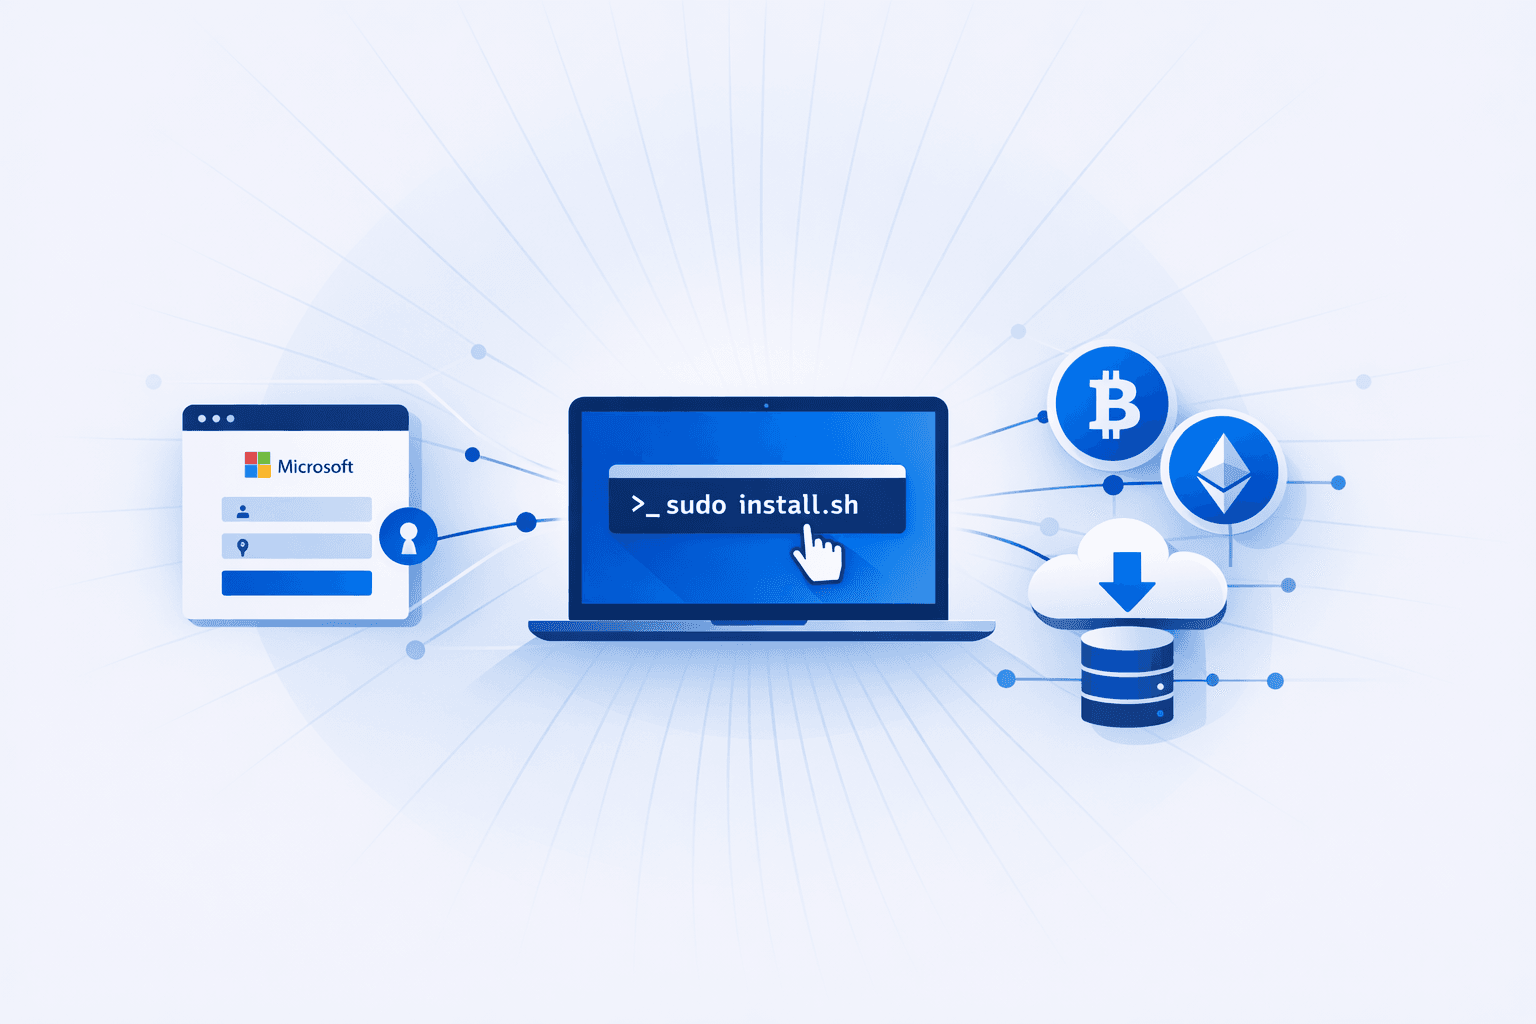
Security researchers reported a **macOS infostealer** dubbed **MacSync** being distributed as a low-cost **Malware-as-a-Service (MaaS)**, primarily targeting **cryptocurrency users** via a *ClickFix*-style social engineering lure. The campaign uses phishing infrastructure (including domains mimicking **Microsoft login** pages) to redirect victims to a fake macOS *cloud storage installer* site that instructs users to “install” by copying and pasting a **single Terminal command**. This approach relies on user execution rather than a signed app package, allowing the infection chain to **bypass macOS protections** such as **Gatekeeper** and **notarization**. Technical analysis describes a **script-based, multi-stage** infection chain: the pasted one-liner fetches a remote script that installs a **daemonized Zsh loader** which detaches from the Terminal session and runs in the background, then retrieves additional payloads (including **AppleScript**) to perform data theft. Beyond credential and wallet data harvesting, reporting indicates MacSync can **persist and expand impact** by **trojanizing Electron-based cryptocurrency applications** (e.g., *Ledger Live* and *Trezor Suite*) by overwriting components to present convincing phishing flows designed to capture **PINs** and **recovery phrases**, potentially triggering theft well after the initial compromise.
Jun 29, 2026
MacSync, a malware-as-a-service macOS stealer and remote-access stager, is being distributed through ClickFix social engineering, SEO poisoning, malvertising, compromised websites, and fake software or AI installers that prompt victims to run Terminal commands. Its native 64-bit Mach-O stager daemonizes itself, XOR-decrypts its configuration, downloads an AppleScript stealer from command-and-control (C2) infrastructure, and executes it in memory through `osascript`. The malware targets Keychain records, browser credentials and cookies, SSH keys, messaging sessions, cloud credentials, cryptocurrency wallets, and sensitive files. It archives collected data and exfiltrates it in 10 MB HTTP PUT chunks before deleting local staging artifacts; analyzed samples used `drivinguber.com` as primary C2 infrastructure and newsinweb.com-derived hosts as fallbacks. Public reporting associates MacSync with the earlier Mac.C Stealer and the developer identity “Mentalpositive,” though Russian-language artifacts do not substantiate attribution to a particular actor, syndicate, or affiliate campaign.
Sep 10, 2026
Huntress reported a macOS intrusion in which a user searching Google for Claude installation instructions clicked a sponsored result that led to a weaponized public Claude share on `claude.ai`, ultimately triggering installation of **MacSync**, a stealer and remote-access trojan. The infection chain relied on a pasted command executed by the victim, then fetched a server-side AppleScript payload, prompted for **Full Disk Access**, and harvested browser data, keychain contents, wallet information, and other credentials before installing a persistent Mach-O RAT. Investigators said the malware also deployed a helper component to obtain **Screen Recording** permission, expanding the attacker’s visibility on the host. The campaign used delivery domains `agenticsora[.]com` and `malwareaudit[.]com`, a RAT command-and-control endpoint at `85.206.161[.]241:8443`, and seed-phrase collection domains `main.sdhomeinspectors[.]com` and `main.southcarolinacounselor[.]com`. Huntress found that if cryptocurrency wallet applications including **Ledger Live**, **Ledger Wallet**, or **Trezor Suite** were installed, MacSync trojanized those apps in place to phish recovery seed phrases and exfiltrate them to attacker-controlled infrastructure. The researchers assessed that MacSync shares strong lineage with **AMOS/Atomic Stealer** tradecraft, including Russian-language developer artifacts, but goes further by combining credential theft with persistent remote access, screen capture, and wallet-app rewriting.
Aug 3, 2026