
Loading story…
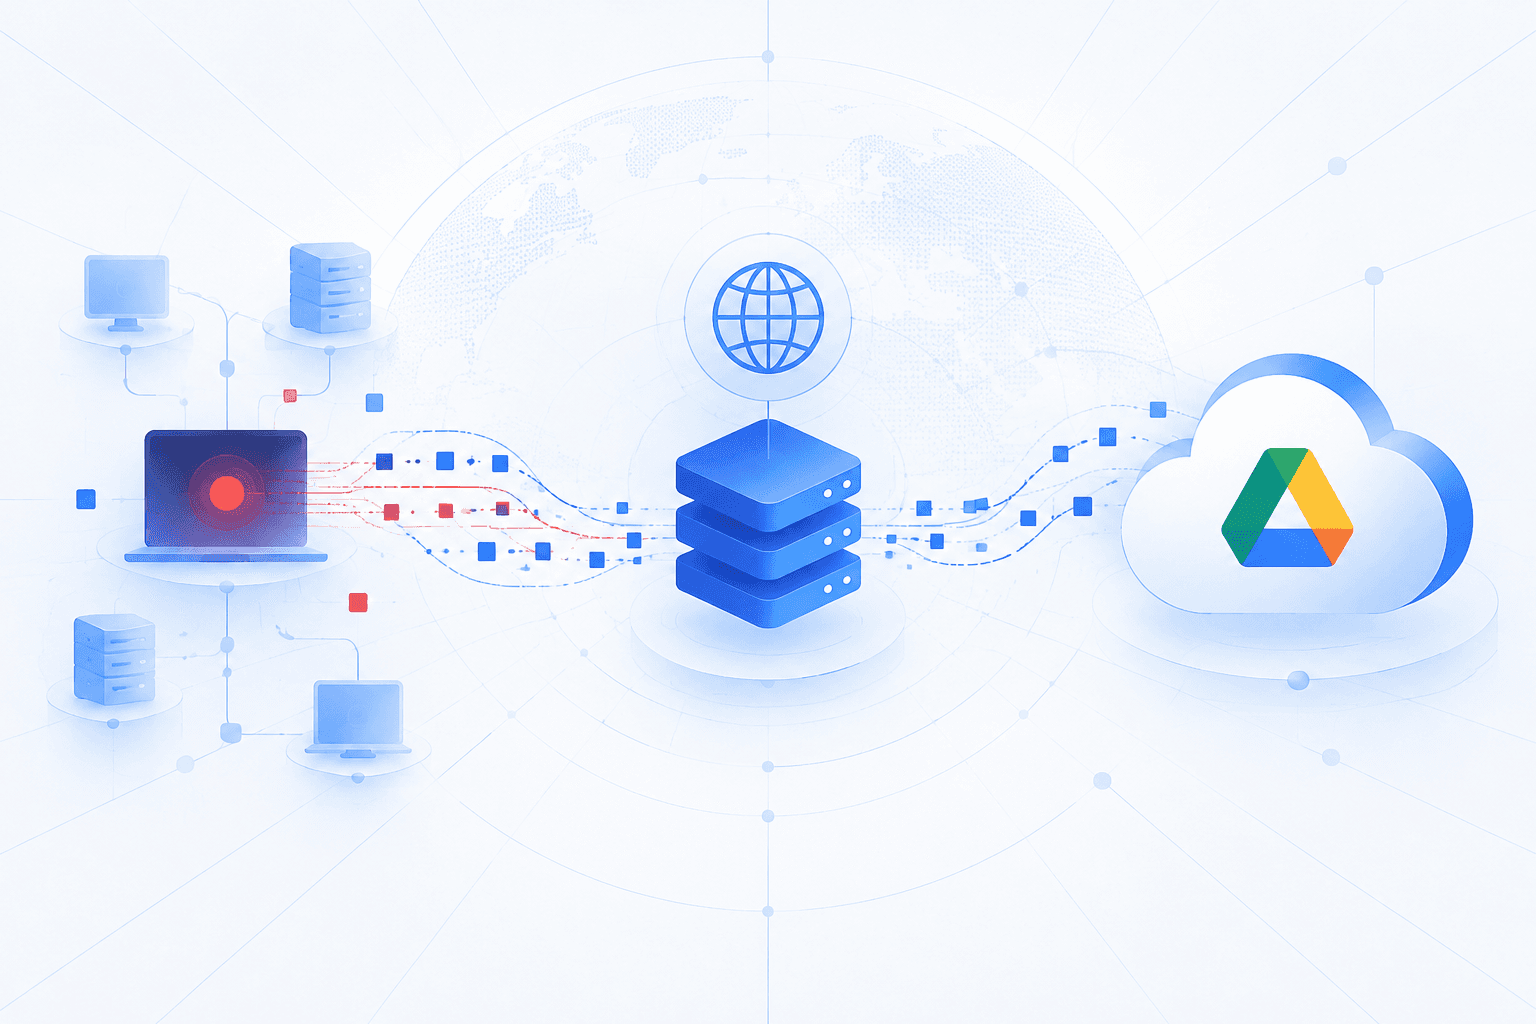
DarkHydrus, also tracked as Lazy Meerkat, targeted politically valuable entities in the Middle East with malicious Arabic-language Excel documents that deployed a C# variant of the RogueRobin Trojan. Researchers obtained the documents on January 9, 2019; embedded VBA macros initiated the infection chain. RogueRobin transmitted stolen system information through DNS tunneling and supported Google Drive as an alternative command-and-control channel through its normally disabled x_mode feature.
The malware included persistence, sandbox and machine detection, and anti-debugging capabilities. The campaign followed earlier DarkHydrus credential-harvesting activity involving Phishery, while reporting also noted suspected use of the Windows remote-code-execution vulnerability CVE-2018-8414—not confirmed exploitation in this infection chain. Defenders should restrict untrusted Office macros, monitor anomalous DNS traffic and unexpected Google Drive access by non-browser processes, and ensure affected Windows systems are patched.
Get the actors, campaigns, and ATT&CK mapping behind it.
3 events from the most recent confirmed update back to the earliest known activity.
The 360 Threat Intelligence Center obtained Arabic-language Excel documents associated with a DarkHydrus campaign targeting politically valuable entities in the Middle East. Embedded VBA macros launched an infection chain that deployed a C# variant of the RogueRobin Trojan.
DarkHydrus, also tracked as Lazy Meerkat, was active by at least 2017. Its historical operations included credential-harvesting campaigns using spear-phishing emails and malicious document templates.
Analysis identified DNS tunneling for transmitting stolen system information and an alternative Google Drive communications channel in the compiled RogueRobin variant. The Google Drive feature, called x_mode, was disabled by default but could be enabled through a command received over DNS.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
Get the adversaries, campaigns, and ATT&CK mapping behind this technique, with detections ready to deploy.
4 references tracked. Mallory keeps watching after this page renders.
zdnet.com
Open sourceunit42.paloaltonetworks.com
Open sourceti.360.net
Open sourceunit42.paloaltonetworks.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
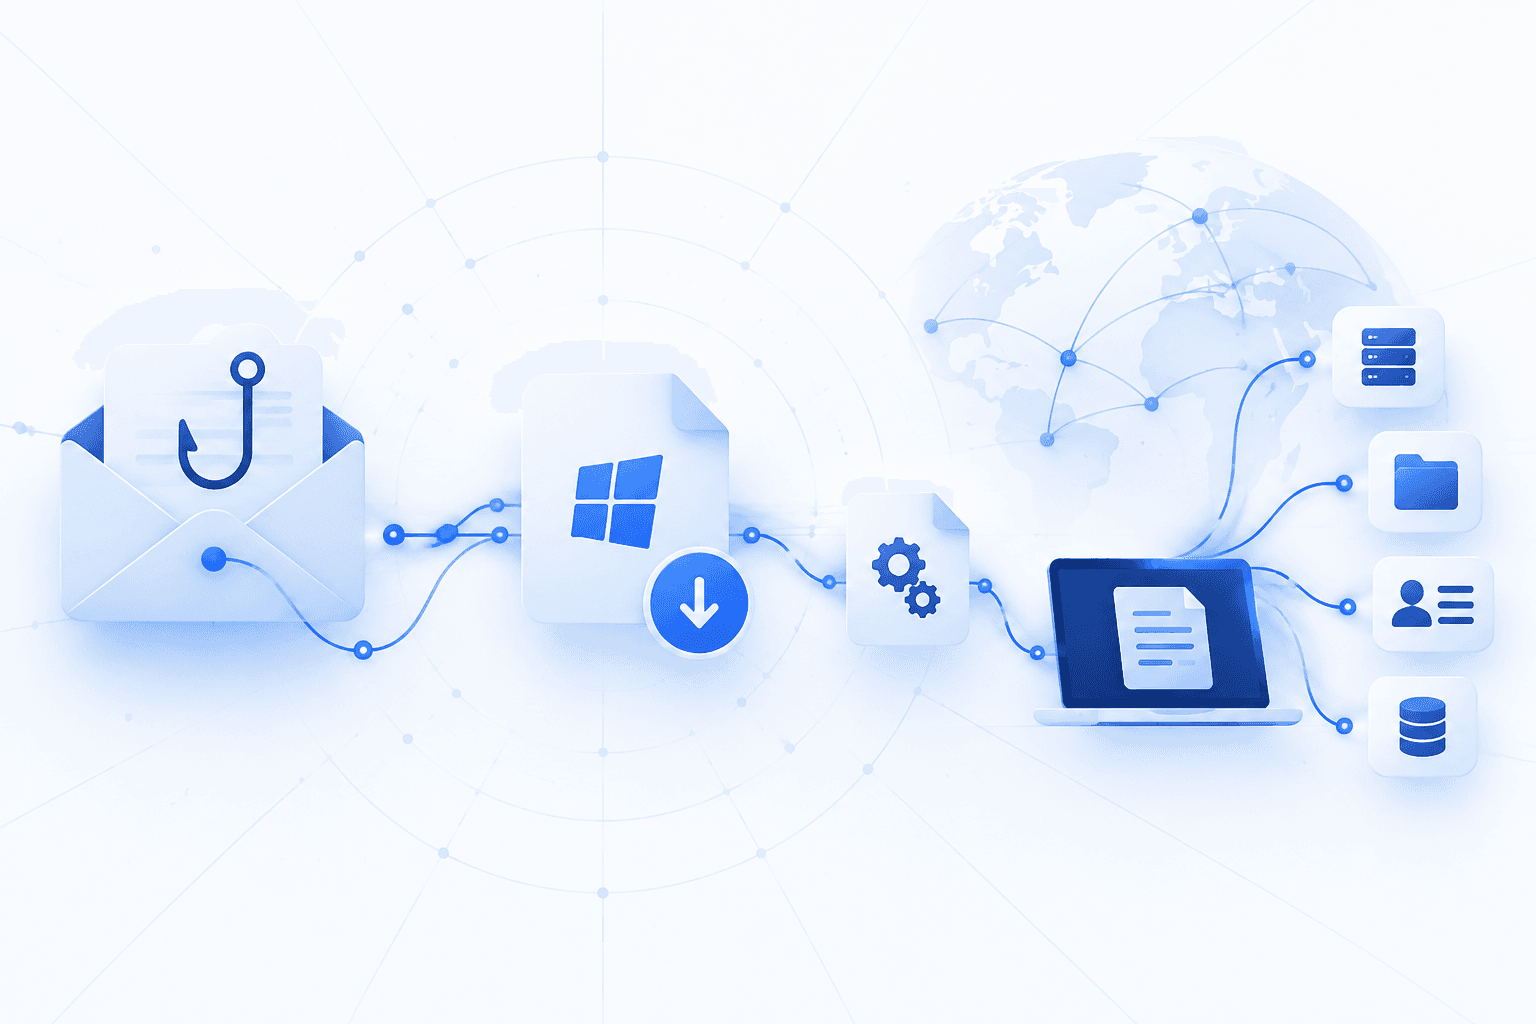
A new **DarkMe** remote-access Trojan campaign has shifted from the exploit-led delivery associated with Water Hydra to straightforward phishing. Lures disguised as image links served executable `.PIF` files, which launched a remote MSI installer and a multistage Visual Basic 6 loader chain. The chain registers a COM object and invokes it through `rundll32.exe /sta {CLSID}`, checks for sandbox-like processes, creates persistence through a custom `Locked://` URI handler, and process-hollows the signed Microsoft `clspack.exe` binary. The final payload combines remote-access and infostealing functions: it can collect cryptocurrency-wallet data, take screenshots, enumerate installed antivirus products, manipulate files, and run commands. It communicates over custom TCP command-and-control on port `7712`; observed infrastructure included `thatawful[.]boutique` resolving to `67.43.50[.]11:7712`. Organizations should block the identified infrastructure, investigate `.PIF` downloads and suspicious remote MSI execution, and hunt for the `rundll32.exe /sta` COM-launch pattern and unauthorized `Locked://` registry protocol handlers.
Sep 25, 2026
Multiple active malware campaigns are using **social engineering** and **trojanized content** to compromise Windows systems, with lures ranging from pirated software downloads to business and shipping documents. AhnLab reported a “proxyjacking” operation attributed to **Larva-25012** that distributes fake installers (notably a trojanized *Notepad++* package) via cracked-software sites; the `Setup.zip` bundle includes a legitimate `Setup.exe` plus a malicious sideloaded DLL (`TextShaping.dll`) that decrypts and installs **DPLoader** for persistent command retrieval and follow-on payload delivery. The malware also tampers with defenses by changing Microsoft Defender settings (e.g., exclusions, reduced notifications, and blocking sample submission) to reduce detection while monetizing victims’ bandwidth through installed **proxyware**. Separately, FortiGuard Labs described a Russia-focused, multi-stage intrusion chain that abuses trusted services (**GitHub** and **Dropbox**) for payload hosting and weaponizes **Defendnot** (a Windows Security Center trust-model research tool) to disable **Microsoft Defender** before deploying a ransomware payload. Fortinet also documented phishing campaigns using weaponized shipping-themed Word documents to deliver **Remcos RAT**, including fileless execution behavior and exploitation of `CVE-2017-11882` (Microsoft Equation Editor) via remotely fetched templates. These campaigns reinforce the operational risk from user-driven execution paths (pirated installers and document lures), “living off the land” techniques, and defense evasion through both policy tampering and security tooling abuse.
Jun 29, 2026
Researchers uncovered an exposed attacker-controlled server that revealed the full workflow behind a WebDAV phishing operation delivering malware through Windows shortcut and signed-binary execution chains. The infrastructure held **1,048 artifacts** including phishing lures, testing notes, admin-panel files, delivery analytics, and documentation that suggested the operator used generative AI tooling to build content and test matrices at scale. The most active campaign impersonated Mexico’s **CURP** identity-record service through the typosquatted domain `gobf[.]mx`, used a WebDAV share on `onedrive[.]cv`, and abused **`CVE-2025-33053`**, a Windows working-directory hijack flaw previously linked to Stealth Falcon activity, to launch a disguised payload posing as a PDF report. The recovered files showed the actor testing **59** `.url` shortcut variants against multiple signed Windows binaries, likely adapting after the original `iediagcmd.exe` technique became less effective on Windows 11 24H2. One infection chain delivered a fileless in-memory **.NET infostealer** that exfiltrated data to `77.110.127.205`, while a second campaign, tracked as **DlrtyGames**, used a 7-Zip SFX dropper, DLL sideloading via a signed Ubisoft binary, IDAT-carried payloads, process hollowing, and persistence to deploy the modular **PureRAT** malware communicating with `23.94.252.228:57666`. Delivery logs from the exposed Simba Service panel recorded **77,098 requests** from **3,892 unique IPs** across **101 countries** over roughly 5.5 days, with activity heavily concentrated in Mexico.
Jul 30, 2026